Otter Vault
- No match
Machine translation — the English original is authoritative.
The Story
Every developer has done it: you generate an API key, the console says "you won't see this again," and it ends up in a .env file, a Slack DM, or a sticky note. I kept losing keys across OpenAI, Stripe, AWS and a dozen other dashboards, so I built Otter Vault.
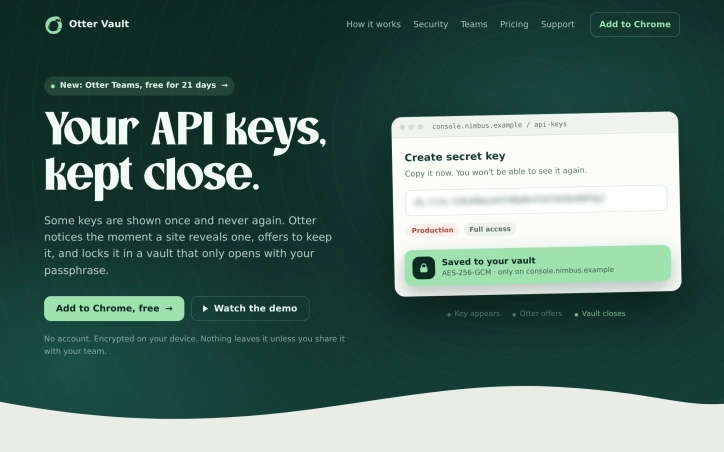
Otter Vault is a Chrome extension that catches API keys the moment they appear on a provider's console and encrypts them on your own device (AES-256-GCM, PBKDF2 with 600,000 rounds). No servers, no account, nothing leaves your machine. It also fills keys and passwords only on the exact origin they were saved from, so lookalike phishing domains get nothing.
The personal vault is free forever. For teams, Otter Teams adds shared encrypted vaults, key mapping, offboarding checklists and activity logs, with a 21-day free trial for up to 10 people. Built solo, tested with 137 tests and a weekly lab across 12 real provider consoles.
AI Overview
AI-generatedAPI key management is a chronic pain point for software teams. Developers routinely generate credentials they never see again, then scatter them across environment files, messaging apps, and scattered notes. Recovery is tedious; tracking where keys are deployed is often impossible; offboarding team members leaves residual access questions unanswered. Otter Vault addresses this problem with a Chrome extension that automatically intercepts API keys at the moment they appear on provider consoles.
The personal vault runs entirely on the user's device. When a key appears, Otter offers to capture it with a single click, encrypting it locally using AES-256-GCM with PBKDF2 key derivation across 600,000 rounds. The passphrase never leaves the device, making recovery by the vendor impossible even if they wanted to provide it. The extension fills keys only on the exact origin they were saved from, rejecting lookalike domains outright. No account creation is required; the entire feature set is free.
What distinguishes Otter from similar offerings is its specificity about security mechanics and its testing rigor. The founder details the exact encryption parameters, the clickjacking protection, and the exact-origin matching rule that prevents phishing. The product is backed by 137 unit tests, seeded fuzzing, cryptographic verification checks, and weekly testing across 12 real provider consoles. The code is public for anyone to audit, removing the need to trust claims.
For teams, Otter offers a second tier called Teams. It introduces a key map that tracks where every shared credential is deployed—which Vercel variable, which GitHub Actions secret, which .env file. When someone leaves the team, Otter re-encrypts all shared keys and generates a checklist of exactly what that person could access and where it lives. Activity logs of all key operations are signed and cannot be tampered with server-side. The trial period is 21 days free for up to 10 developers; the regular price is 29 dollars per month, though an early-bird rate of 20 dollars per month applies through November 13.
The personal vault solves an immediate problem with minimal friction. The team offering adds organizational visibility that most startups lack. For developers who have experienced losing or misplacing credentials, the appeal is straightforward.
Founder Diary
DevlogThe maker hasn't posted a diary entry yet.
Key Features
Chrome Extension Integration
Automatically intercepts and captures API keys at the moment they appear on provider consoles
Local Encryption
Encrypts keys using AES-256-GCM with PBKDF2 key derivation across 600,000 rounds entirely on your device
Origin Verification
Fills keys only on the exact domain they were saved from, rejecting lookalike domains to prevent phishing
Deployment Tracking
Teams feature includes a key map showing where every shared credential is deployed across services
Activity Logging
All key operations are logged with cryptographic signatures that cannot be tampered with server-side
Offboarding Support
Automatically re-encrypts shared keys when team members leave and generates checklists of their access points
Use Cases
-
1
Individual developers
Secure personal API key management without account creation or recovery dependencies
-
2
Software teams
Organizational visibility into where credentials are deployed across Vercel, GitHub, .env files, and other services
-
3
Security audits
Monitor all key operations with signed activity logs and verify compliance with cryptographic checks
-
4
Offboarding workflows
Quickly identify all access points a departing team member had and revoke credentials systematically
FAQ
Do I need an account to use Otter? ▾
How secure is Otter's encryption? ▾
Can Otter protect against phishing? ▾
What happens when someone leaves the team? ▾
Pricing
Personal vault is free indefinitely; Teams tier costs $20/mo through November 13 or $29/mo afterward, with 21-day free trial for up to 10 developers.
Tech Stack & Tags
Discussion (1)

Hey everyone, Krishna here, maker of Otter Vault. I built this after losing one too many API keys to "you won't see this again" screens. Everything is encrypted on your device, with no account and no server. The personal vault is free. Would love to hear which provider consoles you want supported next, and happy to answer any security questions.
Join the conversation — sign up to comment.
Sign up freeCommunity Support
Boost this project on Sell With boost