WinRansomProtect
- No match
Machine translation — the English original is authoritative.
The Story
Ransomware attacks are getting smarter, and most modern antivirus tools rely entirely on the cloud. But what happens when attackers cut your internet connection? You go blind.
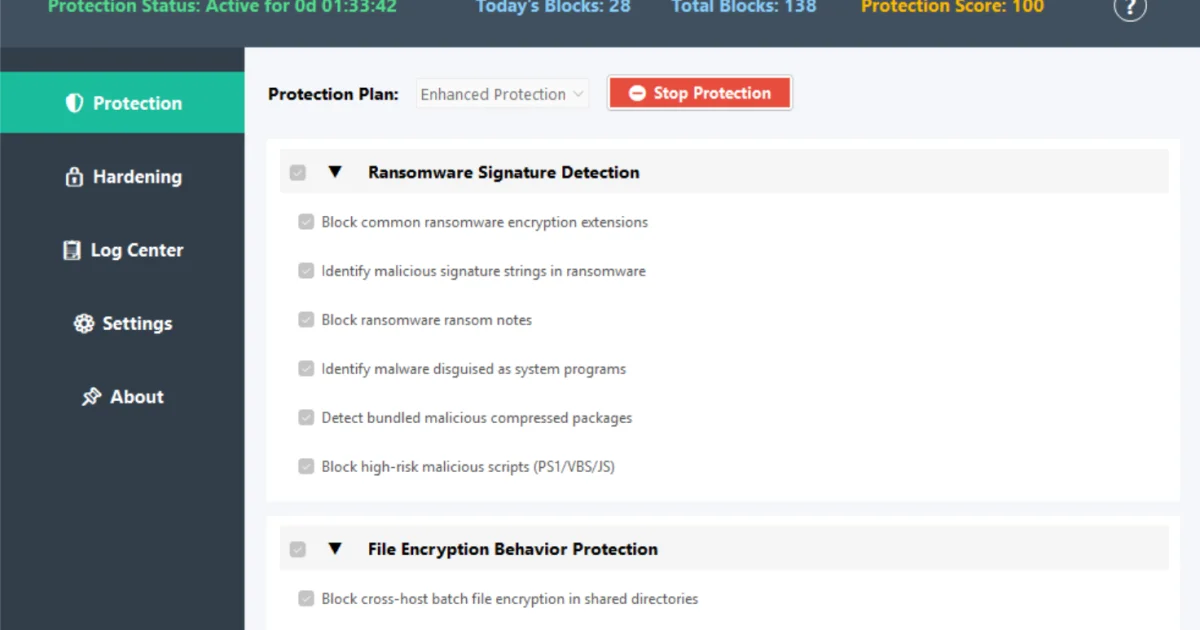
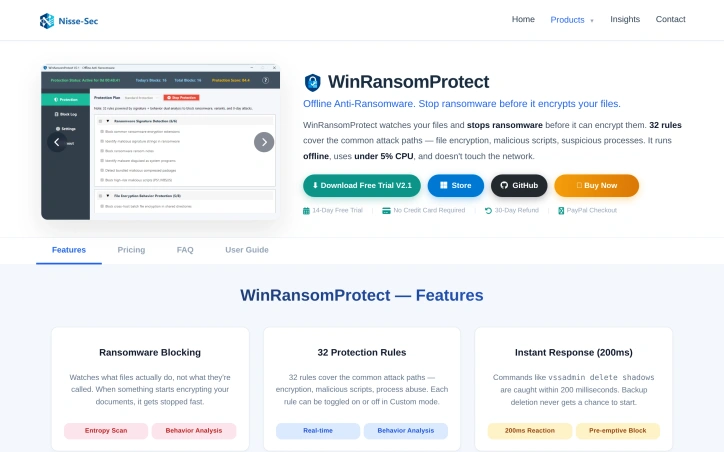
I built WinRansomProtect to solve this. It's a lightweight, 100% offline anti-ransomware tool for Windows. It doesn't need an account, it doesn't send telemetry, and it never touches the network. It just uses 32 local behavioral rules to stop file encryption dead in its tracks before your files are locked.
It's built for home users, freelancers, and small IT teams who need a solid local defense without the bloat of enterprise software.
AI Overview
AI-generatedRansomware threats have evolved beyond what most users understand. While mainstream antivirus solutions depend on cloud connectivity to identify threats, attackers routinely sever network connections as part of their playbook, leaving cloud-dependent defenses useless. WinRansomProtect addresses this gap by delivering local, offline protection designed for users who cannot afford the luxury of relying on network access during an attack.
The product targets home users, freelancers, and small IT teams seeking straightforward defense without the complexity and overhead of enterprise security stacks. The design philosophy is clear: lightweight local analysis beats heavyweight cloud infrastructure when the network itself is compromised.
What distinguishes this tool is its commitment to behavioral analysis without surveillance infrastructure. The product implements 32 rules that monitor actual file system activity rather than relying on file signatures or reputation databases. When encryption activity is detected, the software blocks it within 200 milliseconds, stopping backup deletion and lateral movement attacks through PowerShell and command-line injection before they can gain traction. The monitoring covers high-value directories like Documents, Desktop, and Downloads, flagging bulk operations that exceed normal user patterns.
Beyond ransomware specifically, the tool enforces resource discipline. It operates on under 5 percent CPU and consumes less than 100 MB of memory, which means protection runs continuously without degrading system performance. The absence of telemetry collection or account requirements removes the trust burden entirely. Updates are optional, and the license is hardware-locked, preventing redistribution.
The pricing structure is straightforward: annual plans start at $12.99 per year for single devices, while a one-time lifetime license costs $29.99. Multi-device packages available at $24.99 and $59.99 respectively provide coverage for small operations without requiring annual renewals. A 14-day trial period and 30-day refund policy reduce adoption friction.
The core tradeoff is inherent to the approach: local behavioral detection works well for broad attack categories but lacks the rapid threat intelligence updates that cloud-connected products provide. Users who depend on cutting-edge threat information may find the offline model limiting. For those operating in environments where network disruption is a realistic threat vector, however, WinRansomProtect fills a legitimate defensive gap that larger security vendors have largely abandoned.
Founder Diary
DevlogThe maker hasn't posted a diary entry yet.
Key Features
Local Offline Protection
Delivers ransomware defense that works without relying on cloud connectivity.
Behavioral Analysis
Monitors file system activity using 32 rules to detect encryption attempts rather than relying on signatures.
Fast Threat Response
Blocks encryption activity within 200 milliseconds to prevent backup deletion and lateral movement.
Low Resource Usage
Operates on under 5 percent CPU and consumes less than 100 MB of memory.
No Telemetry
Implements no surveillance infrastructure or telemetry collection and requires no account.
Use Cases
-
1
Home users
Seeking straightforward ransomware defense without the complexity and overhead of enterprise security stacks.
-
2
Freelancers
Need protection that functions when network connectivity is severed by attackers.
-
3
Small IT teams
Require lightweight local protection without enterprise infrastructure overhead.
-
4
Network-disrupted environments
Where network interruption is a realistic threat vector that larger vendors have abandoned.
FAQ
How does WinRansomProtect protect without cloud connectivity? ▾
Does WinRansomProtect slow down my computer? ▾
Does WinRansomProtect collect data about me? ▾
What is the price of WinRansomProtect? ▾
Pricing
Annual subscriptions for single devices with optional lifetime license at $29.99, multi-device packages at $24.99 and $59.99, plus 14-day trial and 30-day refund policy.
Tech Stack & Tags
Discussion
No comments yet — be the first!
Join the conversation — sign up to comment.
Sign up freeCommunity Support
Boost this project on Sell With boost
Meet the Founder
"Independent team building privacy-first, 100% offline security tools for Windows. No cloud, no telem..."
More in Security software
Locksy - Tab Locker & Password Protection
Your browser tabs are a security disaster. Pr...
GeoPatrol
GeoPatrol is a cloud-based SaaS platform that de...
FixMyMacNow
We built FixMyMacNow because Mac users face cons...
Fraudly
We built Fraudly because too many people lose mo...
VeilDB
We built VeilDB because teams need production-li...
Sentinel High-performance surveillance System
Turn webcams and IP cameras into real-time, AI-d...