vibecheck
- No match
Machine translation — the English original is authoritative.
The Story
I built vibecheck because AI-generated code makes the same security mistakes—disabled RLS, exposed secrets, missing auth checks. Generic scanners miss these. We bundle the tools that catch them and triage with AI to explain what actually matters before you ship.
AI Overview
AI-generatedSecurity gaps in AI-generated code follow predictable patterns. Disabled row-level security in Supabase, hardcoded API keys, unauthenticated API routes, and missing CORS boundaries show up repeatedly in code scaffolded by Cursor, Lovable, Bolt, v0, Replit, or Windsurf. Generic vulnerability scanners miss these mistakes because they're not looking for the specific architectural oversights that AI generators tend to produce. Vibecheck fills that gap by bundling gitleaks, semgrep, and njsscan into a single workflow, then using Claude to analyze results and explain what actually matters. Rather than presenting raw scan output, it prioritizes findings by severity and business impact. For developers shipping fast, this triage layer saves hours sorting through false positives.
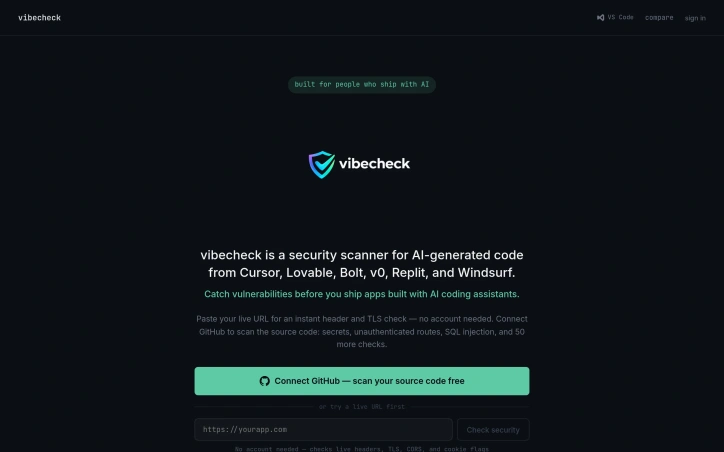
Getting started requires no account. Paste a live URL to check headers, TLS, CORS, and cookie flags immediately. Developers who want to scan source code can connect GitHub and run the full suite of 65 checks across 11 categories: secrets and exposure, access control, injection vulnerabilities, and server-side issues. The VS Code extension allows scanning before deployment without leaving the editor.
The feature set targets real vulnerabilities in rapidly developed applications. Beyond obvious issues like hardcoded JWT tokens or SQL injection, it catches subtle misconfigurations: NEXT_PUBLIC_ secret exposure, Supabase service role keys in client code, GraphQL introspection left enabled in production, and IDOR flaws from missing ownership checks. The 50 custom checks handle patterns that open-source scanners don't catch.
User testimonials reveal substantial value. One developer discovered a completely unsecured Supabase table during a pre-deployment scan. Another runs the scanner against five live products before every deploy, calling it the check they wished existed earlier in their career. The feedback emphasizes that Claude's triage actually reads like human review, not a generic wrapper around existing tools.
The freemium approach—allowing live URL scanning without registration and GitHub integration with no cost—targets independent developers and small teams. The Product Hunt and VS Code Marketplace presence indicate a distribution strategy built for developers who already use AI-assisted code generation.
For teams shipping applications with AI coding assistants, vibecheck addresses a real blindspot in existing security practices.
Founder Diary
DevlogThe maker hasn't posted a diary entry yet.
Key Features
Security Gap Detection
Identifies architectural oversights in AI-generated code by bundling gitleaks, semgrep, and njsscan
Claude-Powered Triage
Prioritizes findings by severity and business impact instead of presenting raw scan output
No-Auth URL Scanning
Check headers, TLS, CORS, and cookie flags on live URLs without creating an account
GitHub Code Scanning
Run 65 checks across 11 categories including secrets, access control, injection vulnerabilities, and server-side issues
VS Code Extension
Scan code before deployment without leaving the editor
Custom Pattern Detection
Catches subtle misconfigurations like NEXT_PUBLIC_ secrets and IDOR flaws that open-source scanners miss
Use Cases
-
1
Developers using AI coding assistants
Addresses security blindspots created by AI-scaffolded code from Cursor, Lovable, Bolt, v0, Replit, or Windsurf
-
2
Fast-shipping teams
Saves hours sorting through false positives by using Claude to triage findings by real business impact
-
3
Independent developers and small teams
Freemium model provides free live URL and GitHub scanning without registration
-
4
Pre-deployment security
Developers run checks before every deploy to catch vulnerabilities like unsecured databases and exposed secrets
FAQ
Do I need an account to use vibecheck? ▾
What vulnerabilities does vibecheck find? ▾
Do I need to pay for GitHub scanning? ▾
Is there a way to scan code before pushing to GitHub? ▾
Pricing
Live URL scanning and GitHub integration available at no cost for independent developers and small teams.
Tech Stack & Tags
Discussion
No comments yet — be the first!
Join the conversation — sign up to comment.
Sign up freeCommunity Support
Boost this project on Sell With boost
Meet the Founder

More by Simon Lane
More in Security software
Locksy - Tab Locker & Password Protection
Your browser tabs are a security disaster. Pr...
GeoPatrol
GeoPatrol is a cloud-based SaaS platform that de...
Fraudly
We built Fraudly because too many people lose mo...
VeilDB
We built VeilDB because teams need production-li...
Sentinel High-performance surveillance System
Turn webcams and IP cameras into real-time, AI-d...
CryptonQR
The Problem: > In an era of constant data breach...