@fuck.it
Email privacy has become an afterthought at mainstream providers, which treat inboxes as data sources to be mined for ad...
Categories
Best Security software Startups & Tools
Security and privacy tools that protect apps, data, and access: threat detection, pentesting, monitoring, passwordless login, and PII vaults.
Recently Listed
26 launches
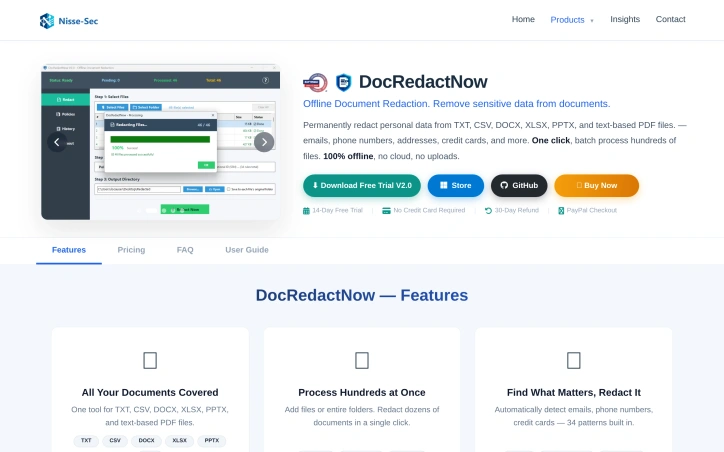
Protecting confidential documents from accidental disclosure has become a critical challenge for organizations of all sizes. DocRedactNow addresses this by offering a desktop application designed to remove sensitive information from files before they leave a user's computer. The core problem the tool targets is straightforward: documents often contain hidden metadata and unnoticed personal data that organizations fail to redact before sharing. Cloud-based alternatives create additional friction by requiring uploads of confidential material to external servers, introducing trust and compliance concerns that many businesses cannot tolerate. DocRedactNow eliminates this trade-off by processing documents entirely offline, ensuring files never leave the user's machine. What distinguishes this product is its practical focus on ease of use combined with local processing. The tool supports six common formats including text files, spreadsheets, presentations, and PDFs, addressing the document types most organizations actually work with. Users can process hundreds of files in a single batch operation, making it suitable for teams managing large volumes of documents. Detection includes 34 built-in patterns covering common sensitive data categories like email addresses, phone numbers, credit card numbers, social security numbers, API keys, and IP addresses. The feature set accommodates both standardized and custom use cases. Pre-built redaction policies cover common compliance frameworks such as GDPR requirements, financial data handling, contract management, and resume preparation. For specialized needs, users can define custom patterns using regular expressions. The application logs all redactions and exports compliance reports, which is valuable for organizations with regulatory requirements to demonstrate data handling practices. The licensing model reflects the offline nature of the product. A perpetual license costs $19.99 as a one-time payment, providing lifetime updates. Annual licensing is available at $9.99 per year for users preferring subscription-based costs. A 14-day trial with full functionality removes purchase risk, and a 30-day refund policy provides additional assurance. DocRedactNow fills a specific niche for organizations prioritizing data protection during document handling while avoiding cloud dependencies. The combination of batch processing, policy-driven redaction, comprehensive logging, and perpetual offline operation makes it a practical choice for teams managing sensitive documents on Windows systems.
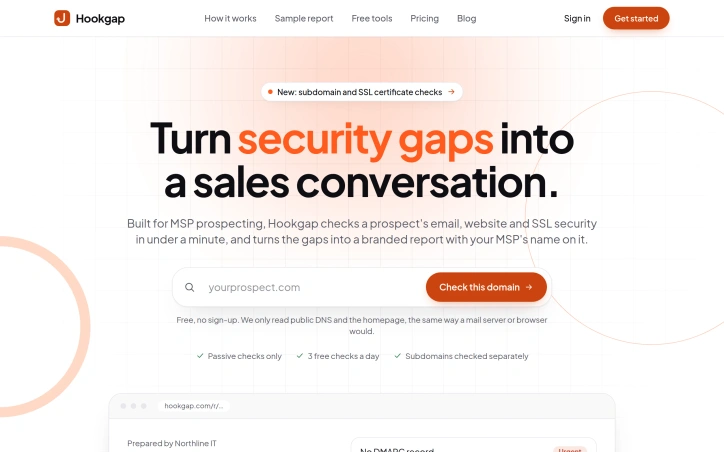
Starting a prospecting conversation with small businesses often requires a concrete reason to call. Hookgap automates security audits of target companies and packages the findings into branded reports that serve as conversation starters for managed service providers and IT consultants. The platform checks a prospect's email security configuration, website settings, SSL certificates, and domain registration status by reading only publicly available data. This passive approach means vendors can run audits before any formal engagement exists. A typical scan completes in under a minute, checking 16 settings across email, web, and domain infrastructure. In a recent sample, the company found that 64 percent of local service firms lacked DMARC records, illustrating how commonly configuration gaps surface in small business environments. What distinguishes Hookgap from generic scanning tools is its focus on prospecting workflow. Users supply their company logo, branding colors, contact information, and booking links; the platform generates a customized report bearing the user's firm's branding. The report identifies specific gaps and severity, from urgent issues like email spoofing vulnerability to less critical items such as publicly visible software versions. Users can share findings as a link or PDF and reference them in email templates and LinkedIn scripts—or a sixty-second video—provided by the platform. This workflow transforms a discovered vulnerability into a justifiable first conversation. The monitoring capability adds follow-up value. After outreach, users can watch a prospect's domain for configuration changes, receiving alerts when certificates expire or new gaps appear. This creates a legitimate reason to reconnect without repeated cold contact. The free tier allows three daily checks with no sign-up required, lowering the barrier to trial. Paid plans remove Hookgap branding from reports entirely, though specific pricing is not disclosed. The design positions the product squarely at service providers who sell infrastructure hardening work—DMARC implementation, certificate management, domain transfer locks—and who benefit from data-driven conversations rather than assumption-based cold calls. For that audience, Hookgap reduces friction between prospect identification and qualified outreach.
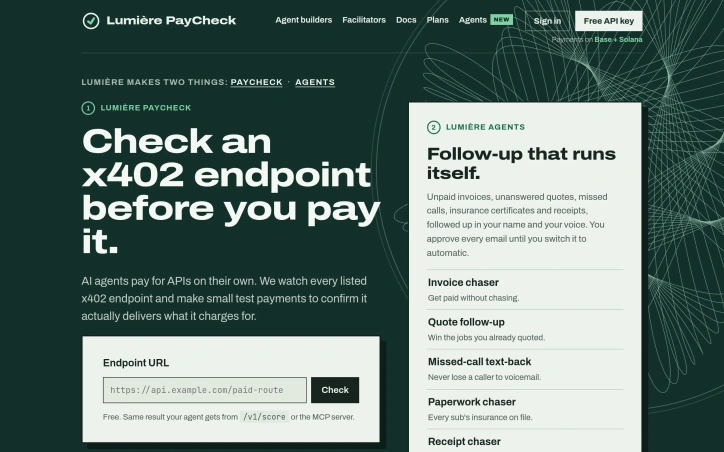
Autonomous API payments introduce a vulnerability: endpoints can fail, return incorrect data, quietly raise prices, or redirect funds to compromised wallets—with agents discovering problems only after transactions settle. Lumière PayCheck addresses this gap by serving as a verification layer that validates x402 endpoints before payment occurs, ensuring agents access services that deliver as promised. The platform monitors roughly 64,000 x402 endpoints across blockchain networks and executes real test payments to confirm endpoint integrity. This active verification approach—checking actual performance rather than relying on passive monitoring—distinguishes the product. Each endpoint receives classification as proceed, caution, or avoid, giving agent builders immediate risk assessment for payment decisions. Integration flexibility removes adoption barriers. The service reaches developers through a free REST API, MCP server compatibility (integrated with Claude and Cursor), or the x402-paycheck npm package. The free tier serves individual developers without payment requirements, while API keys enable higher rate limits for scaling. For teams, Lumière PayCheck adds governance and compliance layers. Features span per-agent spending caps, manual review workflows for unusual payments, signed receipts with full audit trails, and sanctions screening of payout wallet addresses. These additions position the product for finance and compliance operations, not solely development teams. Current monitoring data shows approximately 57,900 endpoints passing validation from a tracked base of 64,000, suggesting substantial adoption within the x402 ecosystem. Team pricing starts at $200 monthly plus $750 setup, with bundled agent features at $500 monthly plus $2,000 setup. This cost structure targets organizations automating invoicing, quote follow-ups, missed-call management, insurance verification, and receipt tracking.
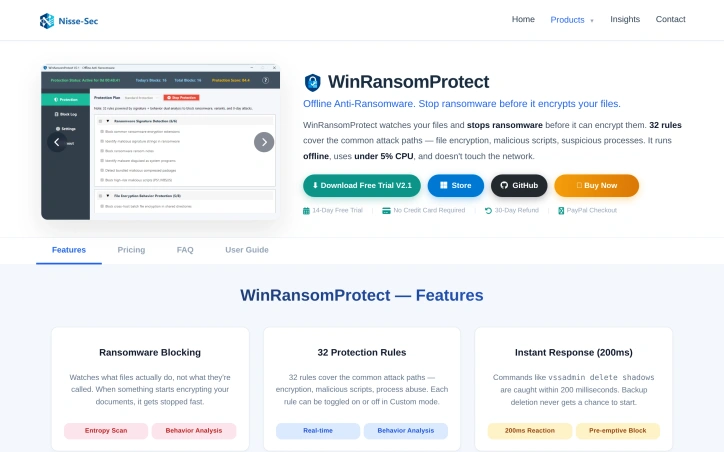
Ransomware threats have evolved beyond what most users understand. While mainstream antivirus solutions depend on cloud connectivity to identify threats, attackers routinely sever network connections as part of their playbook, leaving cloud-dependent defenses useless. WinRansomProtect addresses this gap by delivering local, offline protection designed for users who cannot afford the luxury of relying on network access during an attack. The product targets home users, freelancers, and small IT teams seeking straightforward defense without the complexity and overhead of enterprise security stacks. The design philosophy is clear: lightweight local analysis beats heavyweight cloud infrastructure when the network itself is compromised. What distinguishes this tool is its commitment to behavioral analysis without surveillance infrastructure. The product implements 32 rules that monitor actual file system activity rather than relying on file signatures or reputation databases. When encryption activity is detected, the software blocks it within 200 milliseconds, stopping backup deletion and lateral movement attacks through PowerShell and command-line injection before they can gain traction. The monitoring covers high-value directories like Documents, Desktop, and Downloads, flagging bulk operations that exceed normal user patterns. Beyond ransomware specifically, the tool enforces resource discipline. It operates on under 5 percent CPU and consumes less than 100 MB of memory, which means protection runs continuously without degrading system performance. The absence of telemetry collection or account requirements removes the trust burden entirely. Updates are optional, and the license is hardware-locked, preventing redistribution. The pricing structure is straightforward: annual plans start at $12.99 per year for single devices, while a one-time lifetime license costs $29.99. Multi-device packages available at $24.99 and $59.99 respectively provide coverage for small operations without requiring annual renewals. A 14-day trial period and 30-day refund policy reduce adoption friction. The core tradeoff is inherent to the approach: local behavioral detection works well for broad attack categories but lacks the rapid threat intelligence updates that cloud-connected products provide. Users who depend on cutting-edge threat information may find the offline model limiting. For those operating in environments where network disruption is a realistic threat vector, however, WinRansomProtect fills a legitimate defensive gap that larger security vendors have largely abandoned.
Clipboard interception represents an often-overlooked attack surface in developer workflows. Most security tools catch secrets after they've leaked—in logs, repositories, or cloud environments. PasteGuard addresses a gap in that defensive chain by protecting sensitive data at the moment of paste, before an accidental action becomes a security incident. The product targets individual developers, professionals, and organizations who want to prevent credential exposure during normal copy-paste operations across Windows applications. It detects passwords, API keys, access tokens, cloud credentials, connection strings, and private keys using local detection rather than cloud services. What distinguishes PasteGuard is its commitment to local-first processing. The detection engine runs on the device itself without uploading clipboard content to external services. This privacy-by-design approach acknowledges that clipboard content is inherently sensitive and warrants protection at the source. The product ships with 101 secret detectors covering cloud platforms, databases, source control, DevOps tools, SaaS products, and AI services. The workflow is straightforward. PasteGuard monitors clipboard changes in the background without disrupting normal copy behavior. When sensitive content is detected, it applies protection based on user configuration: warning the user, sanitizing the content, or allowing the paste if the destination application is whitelisted as trusted. A local activity history lets users review what the protection layer has intercepted. The product strategy reflects pragmatism about adoption barriers. Rather than forcing trial periods on users, the free tier offers permanent access to core secret detection, safe paste workflows, and multiple protection modes. The paid Pro edition adds advanced rule control and workflow customization for professionals who need fine-grained configuration. Organizations can deploy consistent PasteGuard setup across managed devices. The product emerged from a real security incident where a credential was accidentally pasted into the wrong destination during routine developer work. Rather than solving credential leakage after exposure, the founder recognized that prevention at the clipboard level was more practical than rotation and incident response. PasteGuard fills a specific but meaningful security gap. It solves a problem that occurs frequently in developer workflows and shields against the easiest mistakes. The local-first architecture removes friction that might otherwise prevent adoption. For teams where accidental secret exposure represents a genuine risk, PasteGuard provides direct defense at a leverage point in the copy-paste chain.
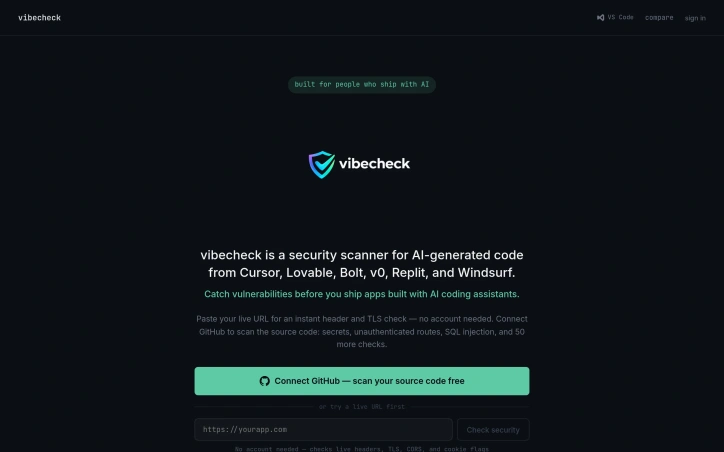
Security gaps in AI-generated code follow predictable patterns. Disabled row-level security in Supabase, hardcoded API keys, unauthenticated API routes, and missing CORS boundaries show up repeatedly in code scaffolded by Cursor, Lovable, Bolt, v0, Replit, or Windsurf. Generic vulnerability scanners miss these mistakes because they're not looking for the specific architectural oversights that AI generators tend to produce. Vibecheck fills that gap by bundling gitleaks, semgrep, and njsscan into a single workflow, then using Claude to analyze results and explain what actually matters. Rather than presenting raw scan output, it prioritizes findings by severity and business impact. For developers shipping fast, this triage layer saves hours sorting through false positives. Getting started requires no account. Paste a live URL to check headers, TLS, CORS, and cookie flags immediately. Developers who want to scan source code can connect GitHub and run the full suite of 65 checks across 11 categories: secrets and exposure, access control, injection vulnerabilities, and server-side issues. The VS Code extension allows scanning before deployment without leaving the editor. The feature set targets real vulnerabilities in rapidly developed applications. Beyond obvious issues like hardcoded JWT tokens or SQL injection, it catches subtle misconfigurations: NEXT_PUBLIC_ secret exposure, Supabase service role keys in client code, GraphQL introspection left enabled in production, and IDOR flaws from missing ownership checks. The 50 custom checks handle patterns that open-source scanners don't catch. User testimonials reveal substantial value. One developer discovered a completely unsecured Supabase table during a pre-deployment scan. Another runs the scanner against five live products before every deploy, calling it the check they wished existed earlier in their career. The feedback emphasizes that Claude's triage actually reads like human review, not a generic wrapper around existing tools. The freemium approach—allowing live URL scanning without registration and GitHub integration with no cost—targets independent developers and small teams. The Product Hunt and VS Code Marketplace presence indicate a distribution strategy built for developers who already use AI-assisted code generation. For teams shipping applications with AI coding assistants, vibecheck addresses a real blindspot in existing security practices.
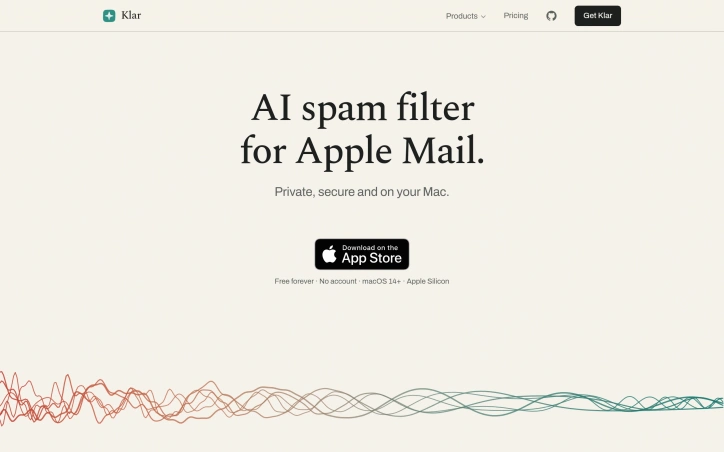
Spam infiltration remains a persistent frustration for email users, despite decades of filter improvements. Klar addresses this gap by applying machine learning directly on the user's Mac rather than relying on cloud servers. This approach prioritizes privacy while handling computational work locally, requiring no account setup or data transmission to external services. The spam problem Klar targets is genuine. Standard email filters from major providers miss substantial amounts of unwanted mail, leaving users manually sorting through clutter. The product targets anyone using Apple Mail who finds existing filters inadequate—whether they use iCloud, Gmail, Outlook, or other IMAP-based email services. What distinguishes Klar is its architectural choice to run the AI model on-device. This design decision carries meaningful implications: messages never leave the user's machine for processing, eliminating concerns about data privacy or third-party access. The absence of mandatory account creation further removes friction and reduces the attack surface for credential theft or data harvesting. The product integrates with multiple email providers, making it accessible to users across different ecosystems. Running locally on macOS means the filter operates within the user's existing email client rather than requiring a separate interface or app switching. The seamless integration reflects Klar's design philosophy—the filter is meant to fade into the background and simply work. The free pricing model removes barriers to adoption. There are no subscription costs, trial periods, or upsells mentioned. This approach prioritizes user acquisition and might reflect confidence in the core filtering technology, though it raises natural questions about long-term sustainability and development resources. The offering is notably straightforward. Klar doesn't claim to reorganize email, learn user preferences through feedback loops, or provide detailed analytics. It does one thing: filter spam with an AI model running locally on your Mac. This focus appeals to users who find existing filters ineffective and want to avoid cloud-based solutions or account requirements. For someone frustrated with Gmail's spam folder or Apple Mail's built-in filter missing obvious junk, Klar presents a technically interesting alternative. The privacy-first local processing model and lack of account friction are genuine advantages. Whether the on-device AI actually performs better than server-side models remains a question only testing can answer, but the architectural approach is sound and user-respecting.
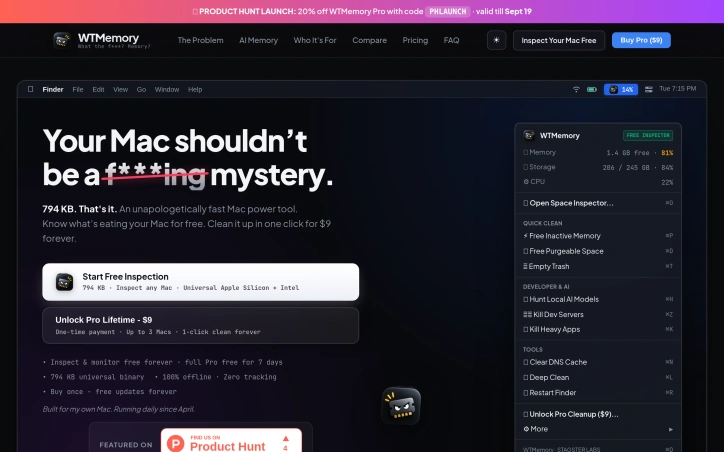
Modern development environments have become invisible performance drains. A developer's Mac accumulates gigabytes of cached machine learning models, orphaned Docker containers, npm package caches, and Xcode build artifacts that legacy system utilities simply don't recognize. WTMemory directly addresses this gap in the market, targeting both everyday users mystified by mysterious slowdowns and developers who understand the problem intimately. What distinguishes WTMemory from conventional Mac cleaning software is its specificity to the modern development stack. Rather than offering vague promises to remove "system junk," the tool directly identifies and clears Ollama model weights, HuggingFace transformer snapshots, Docker virtual disk images, and accumulated npm and pnpm caches. A real-world scan presented on the site identified over 94 gigabytes of recoverable space across these categories alone, demonstrating the scale of the problem WTMemory solves. The product's engineering choices reinforce this focus. At 794 kilobytes, the application is remarkably small, works entirely offline, and tracks nothing about users. It operates as a native Mac utility with a simple interface offering both automatic operations like one-click cleaning of inactive memory and purgeable space, and manual inspection tools. The inspector functionality lets users understand exactly what's consuming storage before committing to cleanup, a useful safety feature when dealing with cached data. The pricing model is straightforward and consumer-friendly. A $9 one-time purchase unlocks the cleaning functions permanently, with free updates included and support for up to three machines. The free tier offers unlimited inspection capability, allowing users to understand their storage situation before paying. The tool's positioning reflects a genuine market gap. As AI tools and local language models become commonplace in development workflows, and as containerization and package management create new classes of hidden storage consumption, the assumptions underlying existing Mac optimization software have become outdated. WTMemory recognizes this explicitly, acknowledging that modern Macs aren't aging so much as becoming exhausted by legitimate workloads legacy tools were never designed to comprehend. For developers accustomed to managing system resources and for everyday users simply frustrated by unexplained slowdowns, WTMemory offers both accessibility and precision.
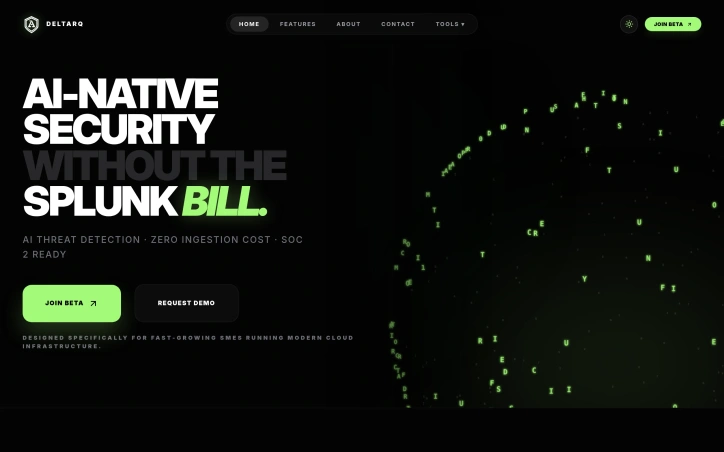
Winning enterprise deals shouldn't require an engineering team to abandon feature development for weeks of compliance busywork. Yet this exact scenario has become routine for startups seeking customers among large organizations that demand SOC 2 certification and exhaustive security questionnaires before signing contracts. DELTARQ targets this friction point with a unified platform combining AI-native threat detection, security operations automation, and compliance management designed specifically for resource-constrained technical teams. The core insight driving the product is sound: traditional security tools divide into two inadequate categories for startups. Enterprise-grade SIEM and SOAR platforms command high costs, lengthy implementation timelines, and require dedicated security personnel to manage alert noise. Compliance software delivers checklists without actually preventing breaches. DELTARQ attempts to collapse this false choice by automating both active threat detection and compliance documentation simultaneously. The product's technical differentiation centers on two commitments. First, it embeds AI throughout its architecture to function as an autonomous security engineer, identifying and blocking network threats without human intervention. Second, it operates entirely within a customer's local infrastructure rather than routing sensitive data through external cloud systems, addressing data residency concerns that often derail enterprise evaluations. For startups navigating sales processes with large customers, this architecture choice eliminates a common objection while reducing the compliance surface area. The platform consolidates three distinct functions—SIEM for log analysis and threat detection, SOAR for automated response workflows, and SOC 2 compliance automation—into a single integration point. This consolidation matters operationally: it reduces deployment complexity and tool proliferation, keeping total cost of ownership low while maintaining enterprise-grade capabilities. The compliance automation piece directly addresses the quantified pain point from the founder's experience: the ability to generate required documentation and evidence automatically rather than through manual effort substantially accelerates enterprise sales cycles. The target customer appears precisely defined: technical teams at SaaS companies that have achieved product-market fit and face enterprise sales requirements but lack dedicated security infrastructure. These organizations typically have the engineering sophistication to deploy and maintain local infrastructure but insufficient scale to justify a full security operations center. The positioning emphasizes pragmatism over comprehensiveness. DELTARQ makes an implicit acknowledgment that startups need adequate security and compliance, not maximum-sophistication security theater. For founders tired of compliance friction, the value proposition translates directly into recovered engineering velocity and shorter sales cycles.
Browser tabs containing bank logins, client files, and sensitive emails remain completely unprotected throughout the workday. Locksy solves this by adding encryption and automatic locking directly within the browser, eliminating the need for traditional password managers or manual security rituals. The product targets anyone who handles confidential information in a browser but finds existing security tools either invasive or inconvenient—remote workers, consultants, and professionals dealing with sensitive client materials fall into this category. Locksy's defining characteristic is its refusal to rely on cloud infrastructure. All encryption happens locally on the user's device, meaning data never leaves the browser itself. This architecture eliminates an entire category of risk that cloud-based competitors cannot escape: the possibility of a central breach, subpoenaed logs, or a company pivoting toward data monetization. The product functions offline, removing dependency on internet connectivity for basic security operations. Auto-locking addresses the behavioral side of security—where users fail to manually protect information. By making protection automatic rather than optional, the product closes the gap between intention and action. The company's bootstrapped foundation shapes its entire approach differently than venture-backed security startups. While competitors pile on features to justify premium subscriptions, Locksy provides free access to core functionality. This reflects confidence in the value proposition and an emphasis on removing adoption friction rather than maximizing revenue per user immediately. The founders articulate their philosophy clearly: they built Locksy out of frustration with security products that sacrifice usability in the name of safety. That focus on combining practical convenience with actual security distinguishes the positioning. Rather than attempting to replace password managers or become an identity platform, Locksy tackles one specific problem exceptionally rather than many problems adequately. The product mentions military-grade encryption, though specifics on cryptographic standards or implementation details aren't disclosed in available materials. For a security product, greater technical transparency would strengthen confidence among informed users, though the offline-first architecture already eliminates major attack surfaces that cloud competitors face. Locksy represents a meaningful attempt to solve a real problem—unprotected browser tabs—without the surveillance capitalist undertones that plague many privacy-focused tools.
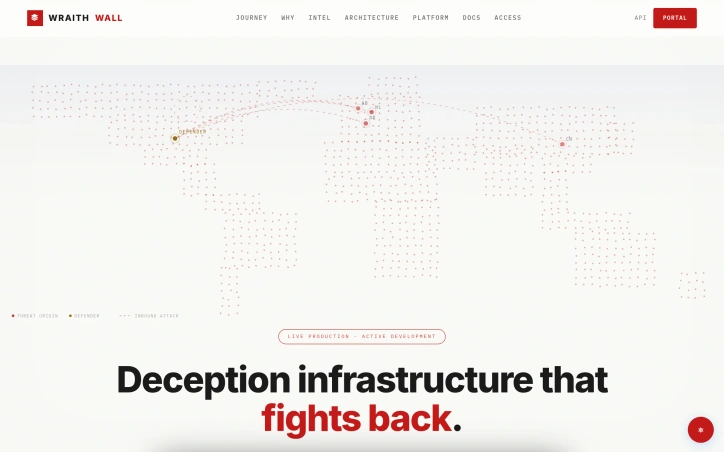
Defensive security has long relied on detection and response, but most tools operate in reactive mode, alerting teams after attackers have already penetrated defenses. WraithWall inverts this logic by embedding deception infrastructure at the perimeter and inside networks, forcing adversaries to reveal their methods before they can reach critical assets. The platform orchestrates honeypots, canaries, credential lures, and BGP monitors as an integrated detection layer. Rather than generating alerts on suspicious activity, these systems capture the full behavioral signature of an attack, including tool choices, timing, payloads, and lateral movement patterns. This evidence feeds a correlation engine that links disparate sessions into campaign clusters, transforming isolated alerts into forensically sound incident narratives. What distinguishes WraithWall from traditional honeypot projects is its claim to operate as a live production system rather than an isolated research environment. The website displays real telemetry from an operational deployment, including threat counts, session captures, and canary triggers. A documented case from May 2026 illustrates this model in practice: when the Cowrie SSH honeypot detected six high-severity sessions within eight minutes, the platform correlated identical payloads and authorized keys modifications across source IPs to identify a coordinated worm campaign rather than six independent attacks. This jump from signal-to-noise reduction to campaign attribution represents the core value proposition. The platform prioritizes evidence integrity and operator transparency. Logs are marked immutable, session telemetry includes fingerprinting through JA3 hashes and HASSH profiles, and findings are mapped to MITRE tactics to improve clarity for downstream incident handlers. By design, deception engagement eliminates false positives that plague production alerts: if a canary or honeypot responds, an attacker has interacted with it, removing guesswork. The attacker journey visualization sequences this data into a coherent narrative across reconnaissance, interaction, deception engagement, correlation, and intelligence output. This staged model acknowledges that not all threats move through every phase and that correlation quality depends on capturing behavior across multiple touch points. WraithWall positions itself for security teams prioritizing attribution accuracy and forensic quality over alert volume, targeting organizations running mature incident response practices. Pricing and licensing details are not disclosed in public materials.
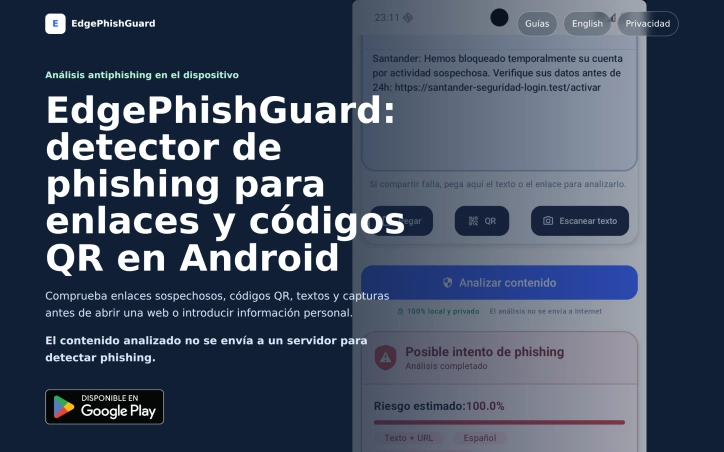
Mobile phishing campaigns have moved beyond simple email tricks. They arrive as text messages that impersonate banks, QR codes that redirect to credential-harvesting pages, notifications from seemingly trusted apps, and links embedded in screenshots shared across messaging platforms. EdgePhishGuard tackles this expanding threat surface by placing a security checkpoint directly on the user's Android device, where the decision happens fastest. The product addresses a genuine gap in mobile security. Most anti-phishing solutions operate on the server side, requiring users to upload suspicious content to cloud services before they get a verdict. EdgePhishGuard inverts this model. Its core analysis runs locally using TensorFlow Lite models that identify linguistic and structural phishing patterns without leaving the device. The approach protects privacy while reducing latency and eliminating friction. What distinguishes this tool is its breadth of input modes. Users can paste suspicious links or text directly, scan QR codes through the camera, extract URLs from screenshots via OCR, or share content from notification bars and messaging apps. This multi-modal design acknowledges how phishing actually reaches people in practice: rarely as a bare URL, often embedded in context that requires extraction or interpretation. The OCR and QR reading capabilities transform the app from a link validator into a content analyzer that handles the obfuscation tactics modern attackers use. The product doesn't attempt to make decisions for users. Instead, it surfaces the reasoning behind its risk assessment, showing detected language, identified patterns, domain reputation signals, and specific recommendations. Users can adjust the alert threshold themselves, creating a control mechanism rather than an on-off switch. This approach aligns with security best practices that favor informed decision-making over black-box automation. Support for multiple languages, with language detection routing content to the appropriate local model, suggests consideration for non-English-speaking populations who may face phishing tailored to their linguistic and cultural context. This practical detail distinguishes EdgePhishGuard from larger security platforms that often overlook regional variations in attack patterns. The absence of pricing information on the landing page leaves questions about the business model unanswered. Whether this will be free, subscription-based, or ad-supported matters to potential users considering adoption. Regardless, the local-processing architecture and transparent risk scoring represent a meaningful departure from the surveillance-heavy approach many mobile security tools take. For users skeptical of uploading sensitive information to cloud services, EdgePhishGuard offers a credible alternative.
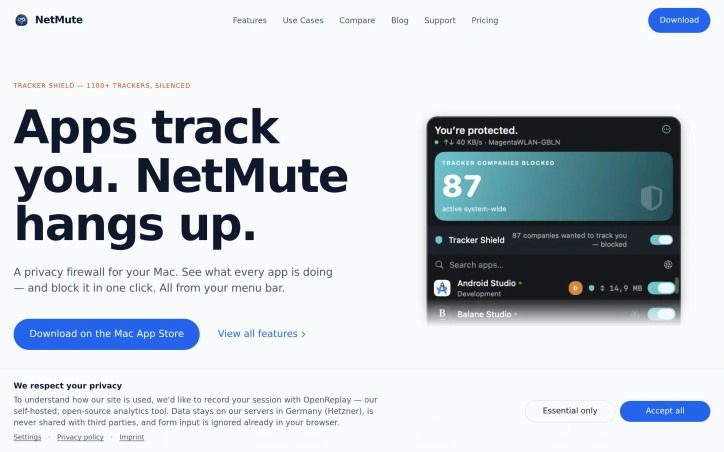
Privacy-conscious Mac users have gained a powerful ally in network management. NetMute addresses a growing frustration among computer users: the invisible background traffic that apps generate constantly, consuming bandwidth and exposing personal data without explicit permission. The core problem is straightforward but often overlooked. Most applications connect to dozens of external services—tracking pixels, analytics platforms, and advertising networks—silently transmitting data throughout your computing session. Users rarely understand the full scope of these connections or how to control them. NetMute surfaces this activity and puts the user in charge. The product offers more than simple blocking. Its Tracker Shield feature silences over 1,100 known tracking services at the network level, from advertising and analytics platforms to social media trackers and fingerprinting services. Rather than requiring users to manually identify and block individual tracking domains, a single toggle activates system-wide protection. The approach extends beyond individual tracker URLs; blocking Facebook's tracking infrastructure blocks all its subdomains automatically. Beyond tracker shielding, NetMute provides granular per-app firewall control. Users can block apps entirely from the internet or surgically disable specific endpoints while keeping others active. The application includes a privacy scoring system that rates each app based on its network behavior, helping users identify particularly intrusive software. Real-time traffic monitoring shows exactly what data flows between apps and external servers, with 90 days of searchable history stored locally on the Mac. Context-aware networking features round out the capability set. Network profiles adapt security settings based on location—stricter rules for untrusted networks like hotel Wi-Fi, looser restrictions for home networks. The software integrates with macOS Focus modes, automatically disconnecting certain apps when focus settings activate. The business model stands out for simplicity: a one-time purchase with no ongoing subscription fees. The app operates locally without requiring cloud services, meaning traffic analysis never leaves your Mac. NetMute targets privacy-focused Mac users who want transparency into app behavior and direct control over network access. It appeals to those frustrated by invisible tracking, users on limited bandwidth connections, and anyone seeking to reclaim network resources currently consumed by background activity. For this audience, NetMute transforms network management from a mysterious background process into an understandable, controllable system.
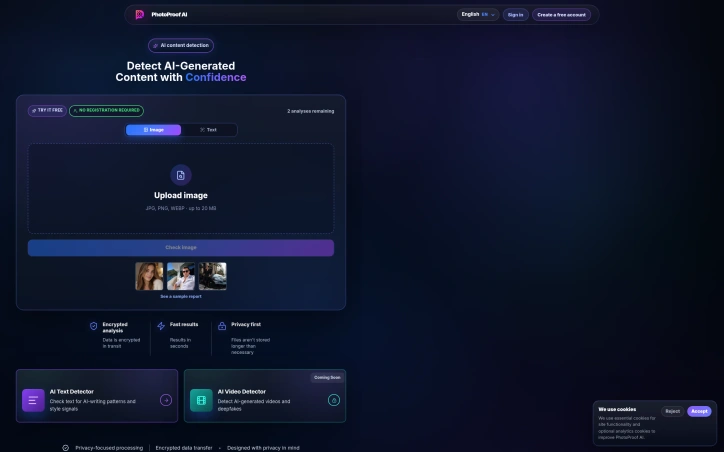
Distinguishing authentic photographs from AI-generated or manipulated content has become a critical challenge as synthetic media proliferates. PhotoProof addresses this need with an automated detection system that evaluates images for signs of artificial generation, editing, deepfaking, and other forms of manipulation. The platform targets a diverse audience: journalists and researchers verifying source material, marketplaces and platforms combating fraudulent listings, educators teaching media literacy, and individuals checking social media profiles or dating app photos. A text detector identifies AI-writing patterns, while video analysis is announced as forthcoming. What differentiates PhotoProof is its multi-layered analytical approach. Every image undergoes five complementary forensic checks: visual pattern analysis searching for synthetic textures and unnatural lighting, metadata inspection examining camera and software records, scene consistency evaluation to identify anatomical or compositional anomalies, source type classification to determine whether an image originated as a camera capture or screenshot, and recompression detection to find traces of editing or manipulation. The system trains on over ten generative models including Midjourney, DALL-E 3, Stable Diffusion, Adobe Firefly, and others. The platform prioritizes speed and privacy. Analysis completes in under 45 seconds. Files are not retained beyond necessity, and all data transfer is encrypted. Rather than presenting definitive verdicts, PhotoProof delivers probabilistic confidence scores with clear explanations of the forensic signals supporting each assessment. The company transparently acknowledges that no detection tool can identify every model with certainty, and that both false positives and false negatives occur. The business model follows a freemium structure. New users receive three free image or text checks without providing credit card information, lowering barriers to casual verification while establishing a path to paid tiers for regular users. This approach allows individuals and organizations to trial the service before committing financially. PhotoProof fills a genuine gap in digital verification for an era where synthetic media rivals authentic photography in quality and distribution speed. The service provides practical forensic analysis accessible to users without specialized expertise in digital forensics, making image verification a realistic task for journalists, investigators, marketplace operators, and concerned individuals alike.
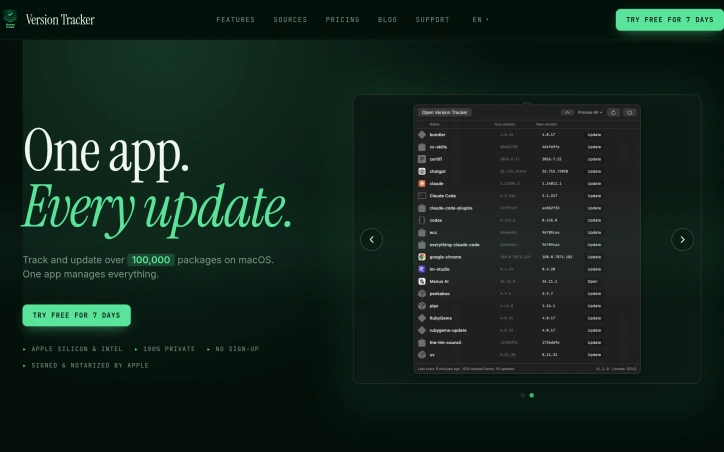
Managing numerous software packages on macOS can be a daunting task, with multiple updates to track and install across various sources. Version Tracker addresses this challenge by providing a unified solution to monitor and update over 100,000 packages, ensuring users stay current with the latest software versions. The developer's primary goal is to simplify the update process, catering to individuals who value staying up-to-date with the latest software releases. By doing so, Version Tracker brings efficiency and security to the forefront, verifying code signing, notarization, and known vulnerabilities for every app. One of the standout aspects of Version Tracker is its comprehensive coverage of various package sources, including package managers, development runtimes, and app updaters. The app integrates data from 47 sources, encompassing Adobe Creative Cloud, npm, pip, Cargo, and many more. This breadth of coverage allows users to manage their entire software ecosystem within a single dashboard. Key features of Version Tracker include a real-time dashboard displaying outdated counts, charts, and categories, as well as one-click updates with progress tracking and auto-removal from the outdated list. The app also prioritizes security, with Apple code signing verification, notarization validation, and CVE database enrichment. Users can try Version Tracker free for 7 days, with no sign-up required. The app is signed and notarized by Apple, ensuring a secure user experience. The developer also highlights that Version Tracker is a natural replacement for MacUpdater, which is now discontinued. Overall, Version Tracker offers a robust solution for managing software updates on macOS, making it an attractive option for individuals seeking to streamline their update process.
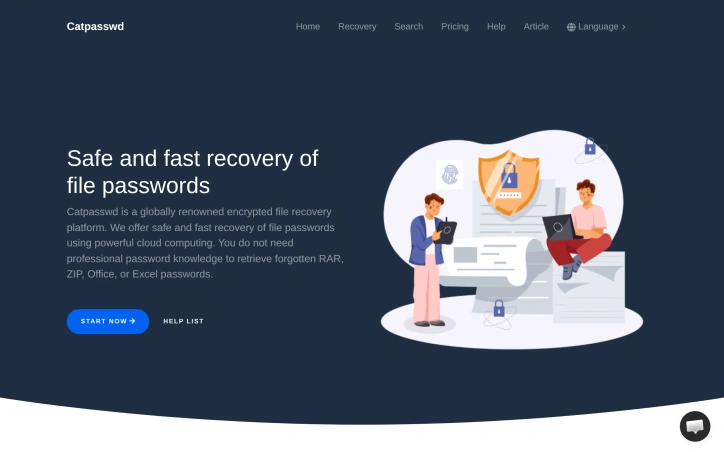
Encrypted file access loss represents a genuine problem for individuals and businesses storing sensitive data in compressed or password-protected formats. Catpasswd targets users who have forgotten passwords or lost access to RAR, ZIP, Microsoft Office, and Excel files—a surprisingly common scenario that often leaves people believing their data is permanently inaccessible. The core value proposition centers on cloud-based password recovery without requiring technical expertise. The platform maintains a database of tens of millions of password combinations, which it uses to attempt recovery matches against users' encrypted files. This crowdsourced password collection approach increases recovery success rates compared to brute-force alternatives, though it also raises implicit trust questions about how these password collections were sourced and secured. The product's standout features are its accessibility and speed. The recovery process appears straightforward enough for non-technical users, with testimonials indicating the service succeeds where other password-cracking tools fail. The existence of a free recovery mode acknowledges users in genuine need, differentiating it from competitors who monetize all recovery attempts. The platform claims to serve over 100,000 users globally, suggesting meaningful product-market fit in an underserved niche. A notable limitation is the scope restriction to specific file formats. Users needing recovery for database files, disk images, or other encrypted containers fall outside Catpasswd's coverage. The reliance on password database matching also means recovery depends on whether the password exists in the company's collection—unusual or recently created passwords may never be recovered, leaving users unaware of this constraint upfront. Pricing details remain absent from available materials. The 100,000-user metric indicates growth, though without churn or retention context it is unclear whether these represent active users or cumulative accounts created. The platform occupies a defensible position in the legitimate password recovery space, distinct from malicious credential-cracking tools. For users facing genuine file access loss, particularly with common passwords, Catpasswd offers a practical alternative to data resignation.
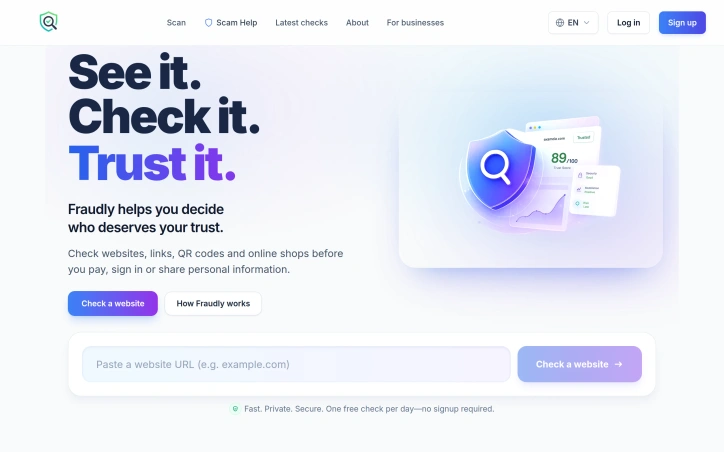
Securing online transactions before they happen addresses a real gap in consumer safety. Fraudly tackles the moment between seeing a link or storefront and deciding whether to trust it with money, credentials, or personal information. The product targets everyday internet users—shoppers, email checkers, QR code scanners, social media link-followers—who encounter suspicious websites constantly but lack reliable tools to evaluate legitimacy in seconds. The core differentiator centers on explainability. Rather than hiding behind opaque risk scores, Fraudly breaks down trust signals across specific dimensions like website safety, business reputation, and shopping intelligence. Users see the reasoning behind each assessment, enabling them to make informed judgments rather than blindly accepting automated warnings. This design philosophy extends beyond marketing; the company explicitly positions itself against unnecessary fear-mongering, acknowledging that not every website fits neatly into safe or unsafe categories. The product reaches users across multiple contexts. The web interface handles website checks with one free analysis daily, no signup required. A mobile app extends functionality to pasted links from messages and emails, QR code scanning in parking lots and cafes, and screenshot analysis—catching suspicious links embedded in images users receive. Browser extensions for Chrome and Microsoft Edge offer passive protection, warning users during normal browsing rather than forcing manual checks. Privacy forms another stated pillar. Unlike many security tools that build detailed browsing profiles, Fraudly commits to not tracking users or commercializing their activity data. This matters because trust products themselves become targets if they collect and monetize user behavior. The Trust Profile synthesizes analysis from multiple established security sources using AI, combining rather than inventing conclusions. The company positions this as stronger than manually researching across separate services. The website reveals little about accuracy rates, false positive performance, or how it handles emerging scams. A sample Trust Profile shows a four-star rating with an 84 confidence score, but public examples don't illuminate edge case handling. The free tier caps users at one daily check, which may frustrate power users or security professionals needing unlimited access. No premium pricing appears on the site. For consumers tired of making trust decisions blindly, the product delivers focused value that explains itself.
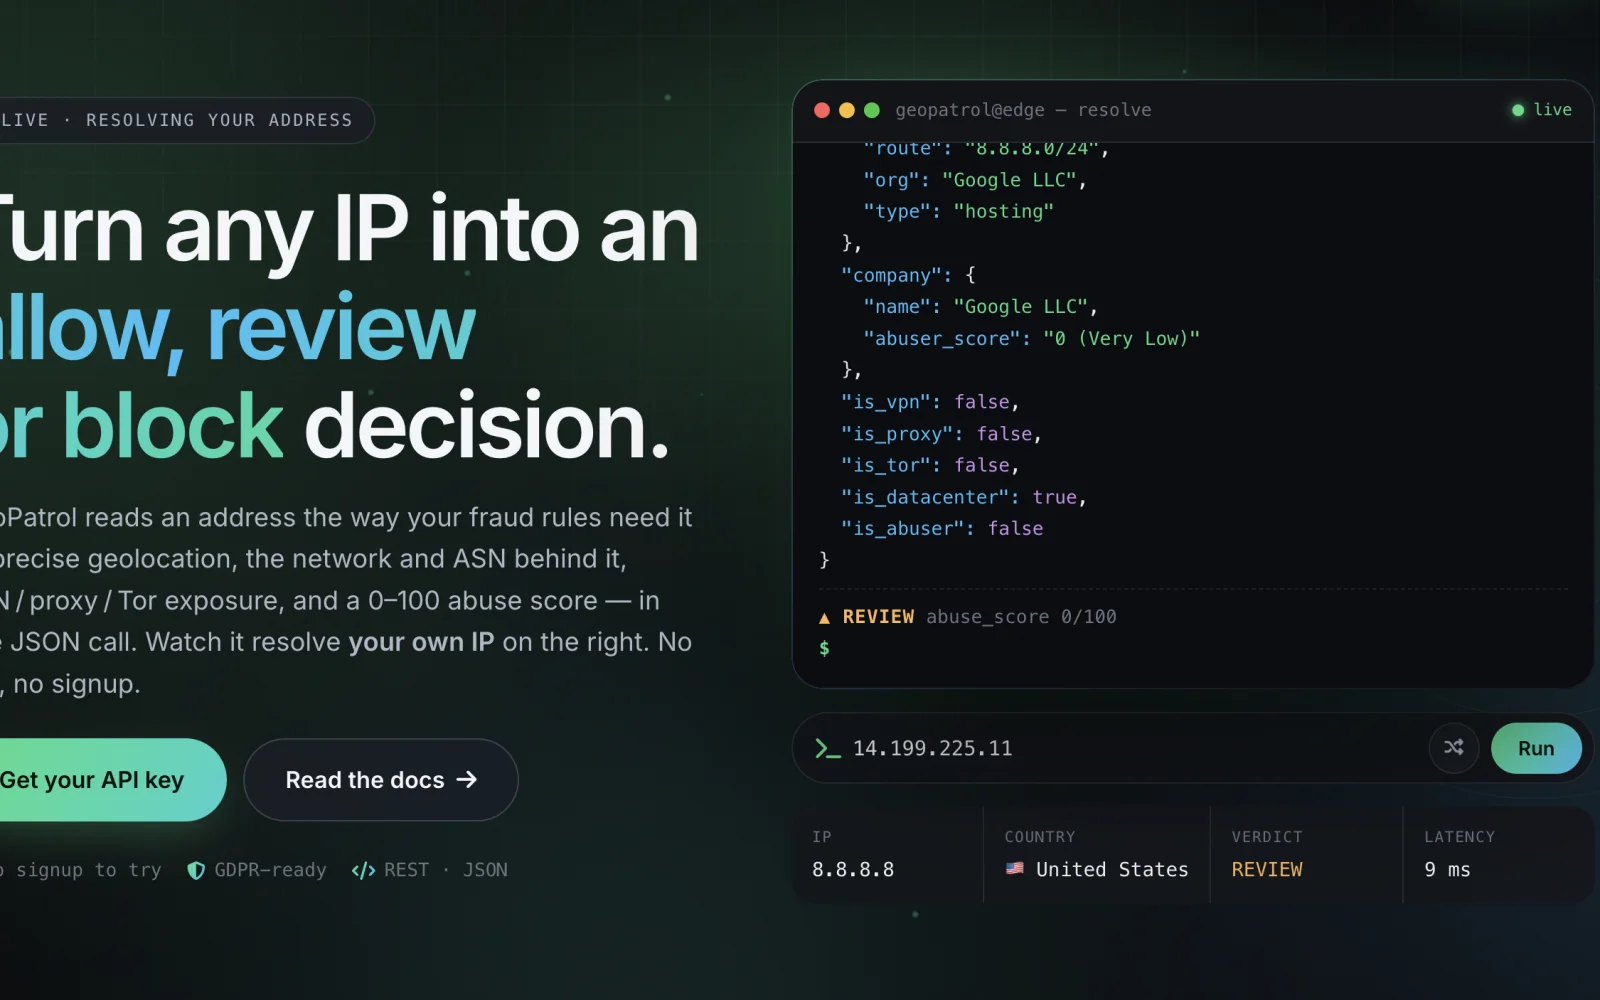
Developers and security teams need to make real-time decisions about incoming IP addresses—whether to allow a transaction, flag it for review, or block it outright. GeoPatrol simplifies this by packaging IP intelligence into a single API call that returns location, network metadata, and a risk score in under 15 milliseconds. The platform stands out through its commitment to live data assembly rather than relying on stale, precompiled databases. Instead of serving old snapshots, GeoPatrol queries routing tables, regional registries, threat feeds, and global probes on each request, then cross-references the results to produce more granular and accurate answers. Published benchmarks claim 99.6% location accuracy and responses in 12 ms at the p95, substantially faster than the 85 ms median from traditional database-driven services. The API returns over 40 data fields per lookup, compared to roughly 15 from typical alternatives. GeoPatrol's feature set is built for fraud and security workflows. Pinpoint geolocation covers city-level precision with latitude, longitude, timezone, and currency. A single 0–100 risk score condenses signals from blocklists, darknet feeds, and historical abuse patterns. Privacy detection flags VPNs, proxies, Tor exits, private relays, and datacenter IPs—critical for identifying obfuscated traffic. Network and ASN data reveal the operator and announced BGP routes behind each address. The platform supports both IPv4 and IPv6. The platform distributes queries across 42 edge nodes globally, delivering sub-15 millisecond responses backed by a 99.99% uptime SLA. The API is designed for compliance, requiring no personal data and offering GDPR-ready, versioned responses with stable field definitions. GeoPatrol operates as a cloud-based SaaS platform billed on recurring subscriptions; specific pricing is not publicly disclosed. A no-signup demo lets prospective users test resolution of their own IP without credentials, reducing friction for evaluation. The product serves businesses handling authentication, payment processing, account security, or fraud-sensitive workflows where understanding an IP's provenance and risk profile directly informs access decisions. Developers find it valuable as a pre-built alternative to assembling intelligence from multiple disparate sources or maintaining custom geolocation infrastructure.
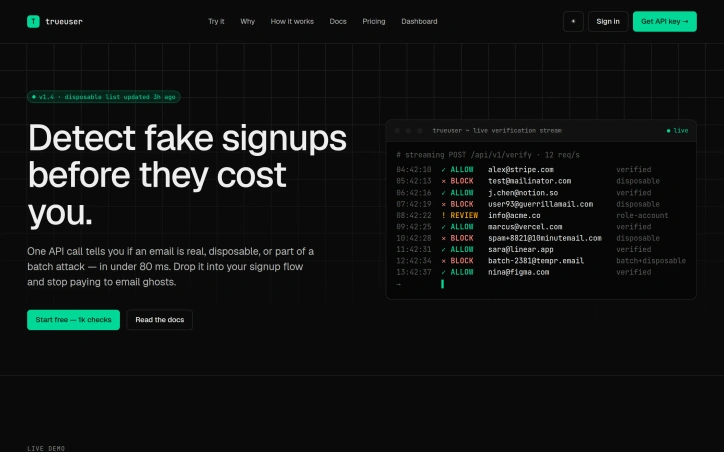
Fraudulent signups remain a persistent issue in the digital landscape, bleeding resources from businesses through unnecessary transactional emails and wasted onboarding efforts. TrueUser offers a solution to this problem with its email verification API, specifically designed for businesses suffering from fake and disposable signups. By integrating TrueUser into their signup flow, companies can verify the authenticity of user email addresses in under 80 milliseconds. What stands out about TrueUser is its comprehensive approach to email verification, checking 14 signals that include disposable domain matching, MX and SMTP probing, and batch-velocity fingerprinting. This robust verification process enables businesses to identify not only disposable email addresses but also coordinated batch signup attacks. The company's dedication to staying ahead of emerging threats is evident in its active tracking of disposable domains, with over 5,439 domains monitored and a list that is updated regularly to include new providers. TrueUser provides businesses with a flexible system, allowing them to either directly use the verdict provided by the API or create their own policy based on the raw signals returned. Every API call is streamed to the company's dashboard, facilitating replay and tuning. The live verification stream demonstrates the API's effectiveness in real-time, showcasing its ability to quickly identify and block suspicious signups. The service starts free, with 1,000 free checks available, indicating a freemium model that allows potential customers to test the API before committing to a paid plan. Overall, TrueUser presents a compelling solution for businesses seeking to mitigate the financial and operational impacts of fake signups.
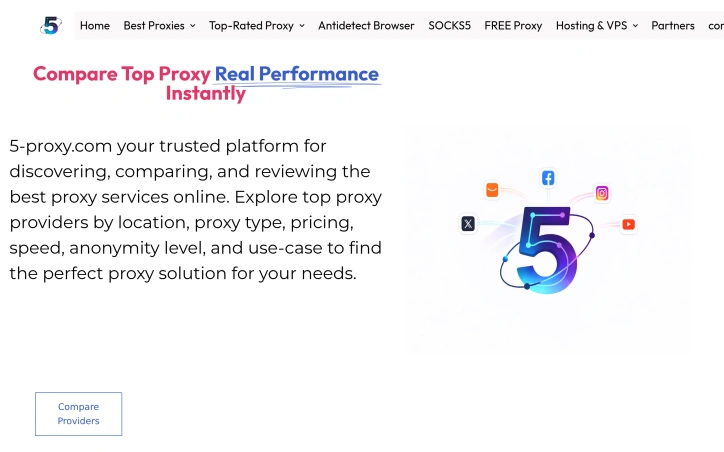
The online proxy market is crowded and complex, making it difficult for users to identify the best proxy services for their specific needs. A new resource has emerged to tackle this issue, providing a comprehensive comparison of top proxy providers. The website is designed for individuals seeking reliable and high-performance proxy services, including those requiring residential, mobile, or datacenter proxies. What stands out about this resource is its curated selection of top proxy providers, hand-picked and ranked based on performance, uptime, and value. The website showcases a diverse range of proxy services, each with its unique features and pricing models. For instance, some providers offer city-level targeting and unlimited threads, while others specialize in 4G/5G mobile proxies or enterprise-grade proxy networks. The website's comparison feature allows users to instantly evaluate top proxy providers based on various criteria, such as location, type, and pricing. The resource also extends beyond proxy services, offering insights into related topics like web hosting and virtual private servers (VPS). The website features a range of hosting options, including lightning-fast SSD hosting, Linux VPS, and Windows VPS, with prices starting at $3.99 per month. Pricing for the proxy services varies, with costs ranging from $1 per IP to $8 per GB, depending on the provider and the specific service. The website's business model is not explicitly stated, but it is clear that it earns revenue through affiliate marketing or referrals, as it promotes various proxy providers and web hosting services. Overall, this resource is a valuable tool for anyone seeking to navigate the complex world of online proxies and related services.